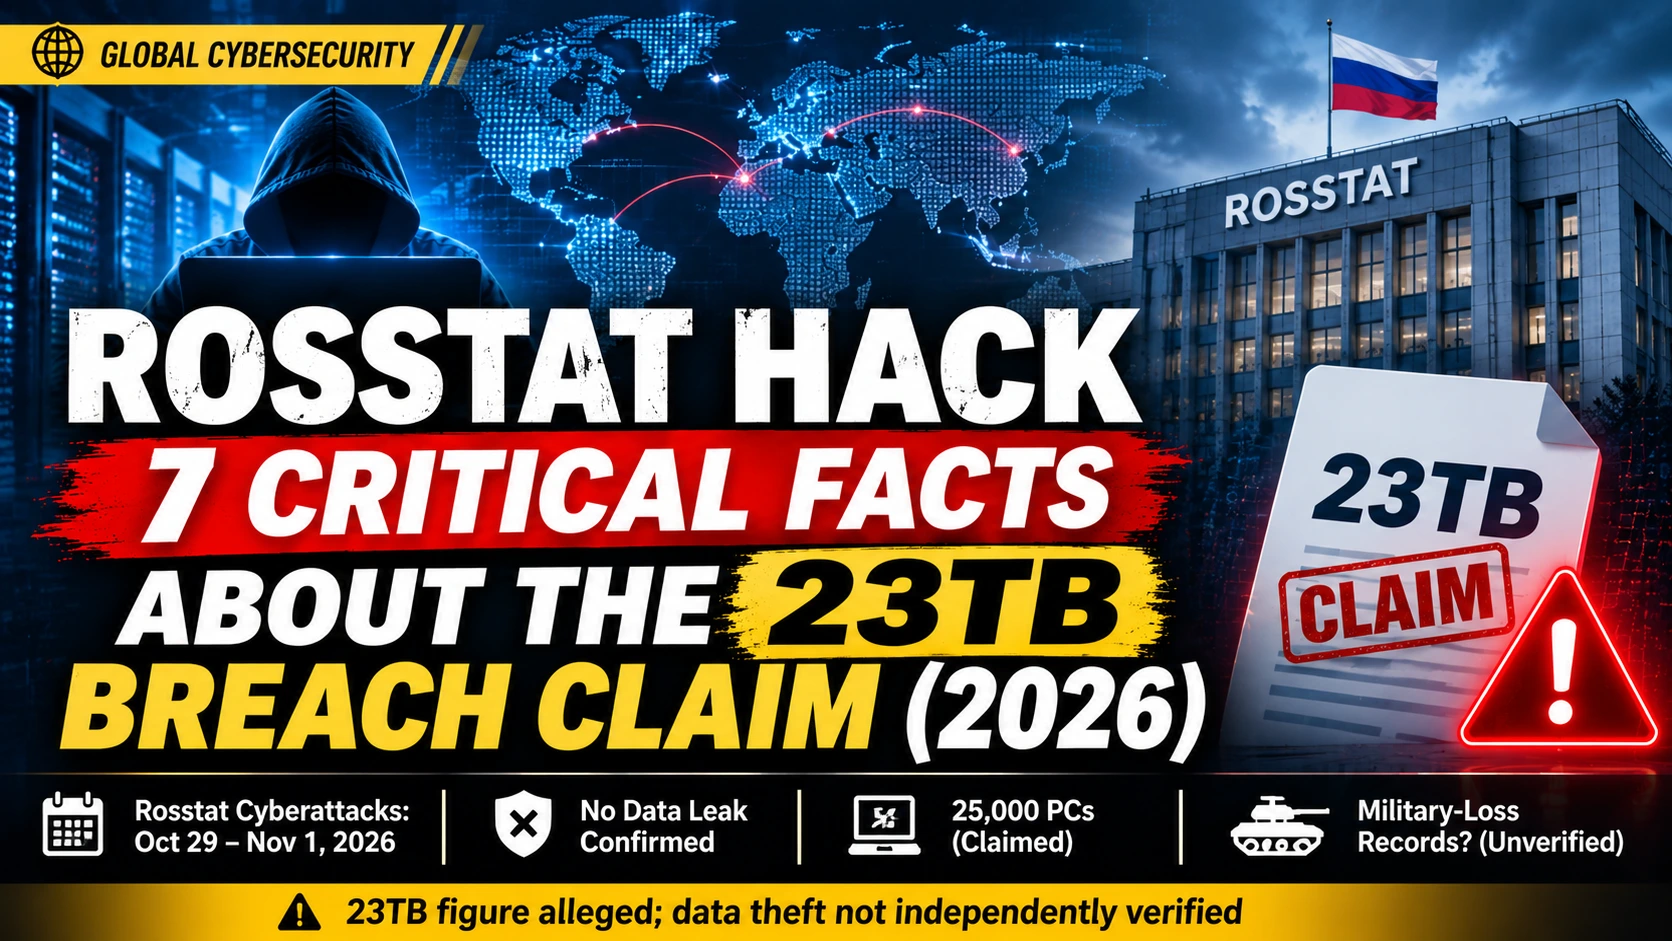
The Rosstat hack is the biggest cyber story in Eastern Europe this week. On 1 November 2026, Belarus’s Cyber Partisans and a group called Silent Crow claimed they stole about 23TB from Russia’s federal statistics agency, including files on Russian military losses in Ukraine. They also say they took control of roughly 25,000 computers and destroyed internal systems. Rosstat confirmed it was attacked. It denied that any protected data leaked.
Most coverage repeats the viral headline and stops there. This guide separates what is confirmed from what is only claimed, so you can discuss the Rosstat hack accurately and avoid spreading numbers nobody has verified. It also explains why the Rosstat hack matters beyond the headline: Rosstat’s data is one of the few public windows into Russia’s war losses.
Here is what you will learn:
- What happened between 29 October and 1 November
- Which Rosstat hack claims are verified and which are not
- Who the attackers are and what they have done before
- Why the stolen files could matter to researchers
- What organizations can learn from the Rosstat hack
We update this Rosstat hack guide as new evidence appears. Last updated: 2 November 2026.
Table of contents
- Fact 1: What Happened in the Rosstat Hack
- Fact 2: What Rosstat Has Confirmed
- Fact 3: Rosstat Hack Claims vs Confirmed Facts
- Fact 4: Who Are Cyber Partisans and Silent Crow?
- Fact 5: Why Rosstat Data on Military Losses Matters
- Fact 6: How Rosstat Hid Its Data Before the Hack
- Fact 7: Security Lessons From the Rosstat Hack
- How to Verify Any Hack Claim
- What Happens Next
- Rosstat Hack FAQ
- Conclusion
Fact 1: What Happened in the Rosstat Hack
The first signs appeared on 29 October. Rosstat’s press service told RBC that its main website was unavailable and would be restored soon. Kommersant reported that hackers had posted a message in Belarusian on the main site and on regional office sites: “No one will escape responsibility.” Logos of Cyber Partisans BY and Silent Crow appeared beside it.
On 1 November the groups went further. Silent Crow said it had “compromised and destroyed” Rosstat’s internal IT infrastructure. It claims access to about 25,000 computers across the central office, regional divisions and the Main Interregional Center for the Processing and Dissemination of Statistical Information. It also says about 2TB of the haul is documents marked for official use.
| Date | Event in the Rosstat hack |
|---|---|
| 1 Nov 2026 | Both groups publish claims. Rosstat confirms targeted attacks and denies a leak |
| By 1 Nov | Belarusian message and group logos appear on the main site and regional portals |
| 29 Oct 2026 | Attacks on Rosstat web resources begin and the main site goes offline |
Fact 2: What Rosstat Has Confirmed
Rosstat has confirmed the cyberattacks. It says its monitoring systems spotted suspicious activity and gave staff time to respond. It places the incident between 29 October and 1 November and says several parts of its online services were targeted.
The agency also denies that databases or legally protected information were exposed. The Moscow Times said it could not independently verify the groups’ claims. So the confirmed part of the Rosstat hack is an attack and a defacement. A proven 23TB theft is not confirmed.
Fact 3: Rosstat Hack Claims vs Confirmed Facts
This is the gap most articles skip. Cyber Partisans wrote of more than 10TB, while Silent Crow says about 23TB, according to Brandefense. That alone shows the numbers are not settled.
| Claim | Who says it | Status |
|---|---|---|
| Website defaced in Belarusian | Media reports, Rosstat acknowledges attacks | Confirmed |
| Targeted cyberattacks, 29 Oct to 1 Nov | Rosstat | Confirmed |
| About 23TB stolen | Silent Crow | Unverified |
| More than 10TB stolen | Cyber Partisans | Unverified |
| About 25,000 computers accessed | Silent Crow | Unverified |
| Internal systems destroyed | Silent Crow | Unverified |
| Files on military losses taken | Both groups | Unverified |
| No protected data leaked | Rosstat | Disputed, no independent check |
Crucially, neither group has released specific casualty figures from the alleged trove. Until samples are published and independently checked, the safest wording for the Rosstat hack is “claimed,” not “stolen.”
Fact 4: Who Are Cyber Partisans and Silent Crow?
Cyber Partisans is a Belarusian hacktivist group opposed to the Lukashenko government. Silent Crow is a pro-Ukrainian hacktivist group. Russian authorities have outlawed both and classed them as extremist, so Russian state media treats their statements as hostile.
Silent Crow’s track record is what gives the Rosstat hack claim weight. In January 2025 it claimed to have taken 2 billion property-owner records from Russia’s land registry, Rosreestr. Journalists later verified sample entries despite official denials. That history makes the Rosstat hack worth taking seriously. It does not prove this specific claim, because each breach has to be verified on its own evidence.
Fact 5: Why Rosstat Data on Military Losses Matters
Ukrainian outlet Ukrinform reported the claim that the hackers obtained data on Russian losses in Ukraine. The groups also say the files include demographic and economic statistics and documents labeled “for official use only.”
That is why the Rosstat hack travelled so fast. Rosstat was once the main public source behind independent excess-mortality analyses of the war. If raw regional files were ever published and verified, researchers could test their loss estimates against them. But nothing has been published yet. Any casualty number attached to the Rosstat hack today is unverified, so treat it with caution.
Fact 6: How Rosstat Hid Its Data Before the Hack
The attack hit an agency that had already been narrowing what it shows the public.
| When | What Rosstat stopped publishing |
|---|---|
| From March 2025 | Regional, then monthly, births and deaths data, according to The Moscow Times |
| July 2024 | Detailed mortality data on external causes, which journalists had used to calculate war deaths |
| 2022 | Military deaths as a separate sub-category |
Even then, researchers found a workaround. Important Stories deduced combat losses from Rosstat’s “unassigned deaths” category, because total deaths still had to be reported. The U.S.-based Institute for the Study of War later linked the data blackout to efforts to obscure personnel losses. Against that background, the Rosstat hack lands on exactly the data people most want to see.
Fact 7: Security Lessons From the Rosstat Hack
Whatever evidence eventually emerges, the Rosstat hack shows how one campaign can mix defacement, data theft and destruction. Any organization can face the same pattern. The Kettering Health ransomware attack showed how quickly a network incident can disrupt daily operations.
What the Rosstat Hack Teaches About Attack Chains
Attackers rarely stop at one weakness. A flaw on a public website can lead to stolen credentials, then to internal machines, then to bulk data. Each stage is a chance to detect and stop them. Rosstat says its monitoring spotted suspicious activity, which is one of the few details both sides agree on.
| Control | Question it answers | Rosstat hack lesson |
|---|---|---|
| Web application penetration testing | Can attackers deface or abuse our sites? | The first visible sign was defaced websites |
| External penetration testing | What can someone on the internet reach? | Initial access usually starts outside |
| Internal infrastructure penetration testing | If they get in, how far can they move? | The groups claim 25,000 machines |
| Network security monitoring | Would we notice in time? | Rosstat says monitoring raised the alarm |
| Backups and incident response plan | Can we recover if systems are wiped? | The groups claim destroyed systems |
Penetration Testing Finds Weaknesses First
Why penetration testing is important comes down to proof. It shows which weaknesses an attacker can actually exploit, not just which ones exist on paper. A professional VAPT service combines a vulnerability assessment with ethical hacking penetration testing, so you receive a ranked list of fixes.
Start with web application penetration testing against the OWASP Top 10 risks. Then add external penetration testing to see what the internet can reach. Follow a recognised method such as the NIST SP 800-115 testing guide and agree the penetration testing scope and rules of engagement in writing.
How Often Should Penetration Testing Be Done?
Test at least once a year and after any major change to your network or applications. Fast-moving products benefit from a continuous pentest. Regulated sectors also need compliance penetration testing and a documented ISO 27001 vulnerability management process.
A test usually takes from several days to a few weeks, depending on scope. The real risk reduction comes after the report. Penetration testing remediation means fixing each finding and retesting it.
Build Detection and Recovery
A security risk assessment tells you which systems matter most. Pair it with network security monitoring and a tested incident response plan. Keep offline backups so a wiper or ransomware attack cannot erase your only copy of critical data. Strong ransomware protection is as much about recovery as prevention.
How to Verify Any Hack Claim Like the Rosstat Hack
Hacktivist claims are often exaggerated, and denials are not proof either. Use this checklist before you share a number.
- Look for samples. Has the group published files that others can check?
- Check the track record. Were the group’s earlier claims later verified?
- Compare the numbers. The 10TB and 23TB figures do not match.
- Wait for independent confirmation from journalists or security firms.
- Treat official denials as one input, not the final word.
If files are ever published, do not download or repost personal data. Cite the reporting instead.
What Happens Next
Watch for four developments. Samples may be released. Independent researchers may verify them. Casualty figures may appear. Rosstat may restore its main site and publish a fuller statement. We will update this Rosstat hack guide when any of these happen.
Rosstat Hack FAQ
Did hackers really steal 23TB from Rosstat?
It is not confirmed. The figure comes from Silent Crow, and Rosstat denies that protected data leaked.
Is the Rosstat hack confirmed?
The attack and the website defacement are confirmed. The 23TB theft and the destroyed systems are not.
Who is behind the Rosstat hack?
Belarus’s Cyber Partisans and the group Silent Crow claimed responsibility. Russia has classed both as extremist.
Has the military loss data been published?
Not as of 2 November 2026. Neither group has released specific Russian casualty figures.
What did Rosstat say?
It said targeted cyberattacks hit its systems between 29 October and 1 November and that no legally protected data was exposed.
Is Rosstat’s website back online?
The main site was unreachable in the first reports. Check the site directly for its current status.
What is a wiper attack?
A wiper attack aims to destroy data and systems rather than steal them or demand a ransom. The groups say they used this approach, but that is unverified.
Conclusion
The Rosstat hack is a confirmed attack wrapped around an unverified claim. The defacement and the cyberattacks are real. The 23TB theft, the 25,000 machines and the military loss files are still only claims. Until samples are checked independently, report them as claims.
The lesson for every organization is practical. If a national statistics agency can be defaced and disrupted, yours can too. Do not wait for a Rosstat hack of your own to find your weak points.
Ready to find your weaknesses before attackers do? Book your VAPT assessment with Nexus Web Security and get a ranked remediation plan for your websites, applications and network.
Sources: Brandefense, EconoTimes, Mezha, Dagens, The Moscow Times, Jamestown.